The lean ISMS for SMEs
- Developed in practice by an information security officer and an ISMS consultant.
- Proven in real certification audits.
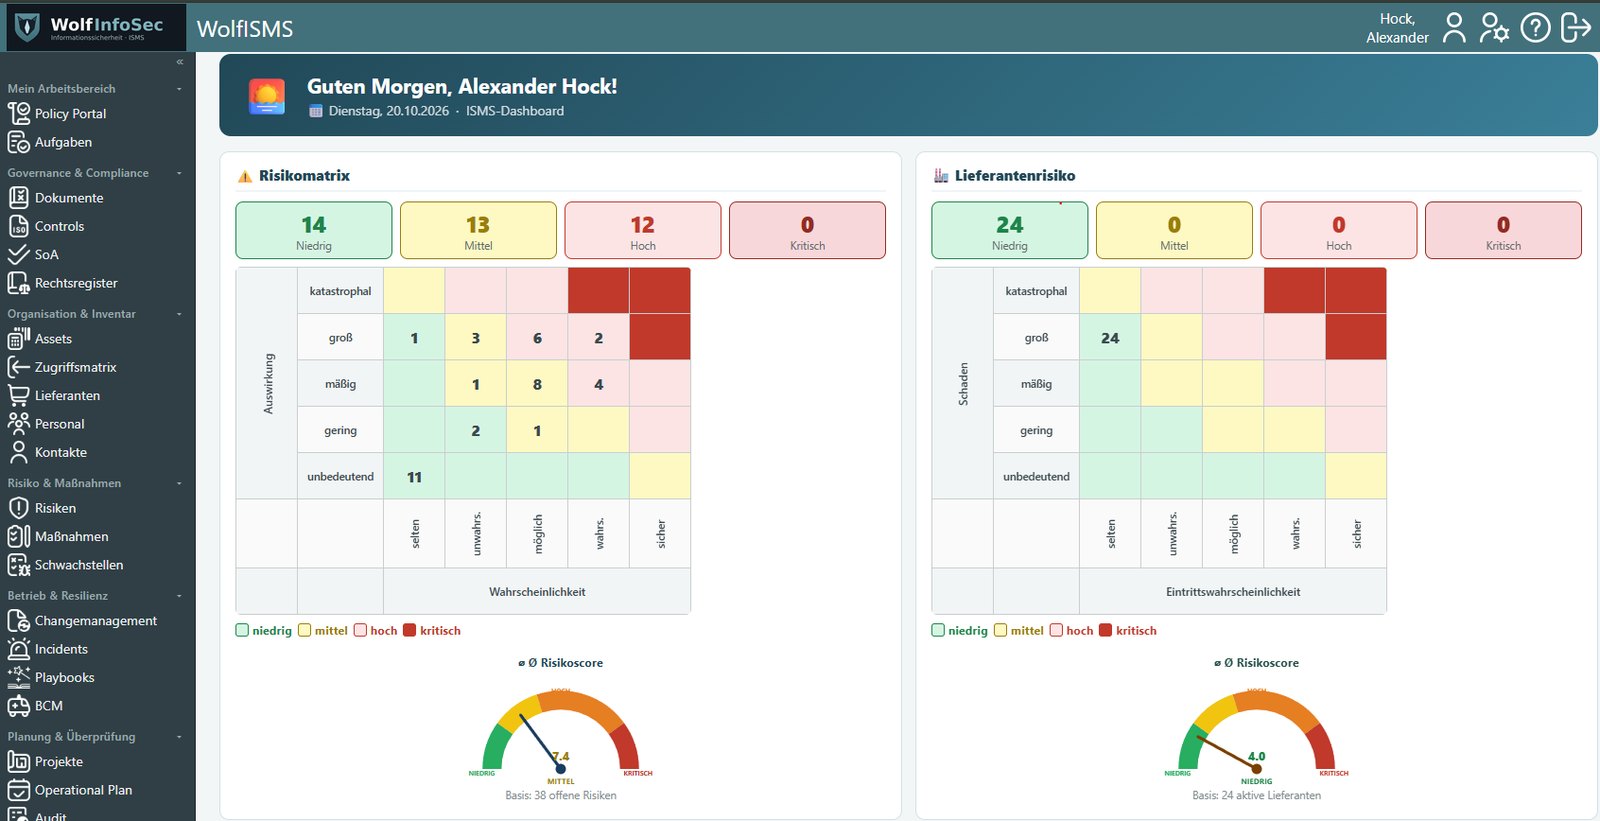
- Equipped with AI assistants that ask follow-up questions like an ISMS consultant and take the legwork off your hands.
- ISO/IEC 27001/27002
- NIS2
- GDPR
- BSI IT-Grundschutz
- CRA
- Cyber Essentials
Excel is not enough. A GRC suite is too much.
Spreadsheets hit their limits
Risks, controls and evidence spread across Excel and SharePoint lose their connections by the time the audit comes round.
GRC suites are oversized
Large platforms take months to roll out and tie up budget that is then missing for actual security.
An ISMS demands evidence
What counts is an ISMS that is lived, documented and above all effective, not just good intentions.
“That is exactly why we built WolfISMS. We needed it ourselves, as an information security officer in a mid-sized company and as consultants on projects. Today it is used by customers and consultants alike: affordable for SMEs, with AI doing the legwork.”
Managing Directors, WolfInfoSec GmbH
More than 20 modules. Each with a clear job.
Governance & documents
- Policy portal
- Documents
- KPIs & objectives
- Management review
Assets & risks
- Asset management
- Risk management
- Vulnerability management
- Access matrix
Implementation & operations
- Measures
- Operational plan
- Change management
- Tasks & deadlines
People & partners
- Personnel management
- Supplier management
- (Emergency) contacts
- Reporting
Incidents & resilience
- Incident management
- Playbooks
- BCM
- Information security in project management
Compliance & evidence
- Standards
- Controls
- Legal register
- Audits
The AI suggests. You decide.
The assistants ask follow-up questions like an ISMS consultant and work right where you are. Nothing is saved without your confirmation. Built in line with the EU AI Act and usable in a GDPR-compliant way with the AI provider of your choice or your own model.
Onboarding dialogue
Sets up your ISMS in a conversation, just like a consultant.
Risk linking
Links risks to threats, controls, assets and suppliers.
Vulnerability search
Finds known vulnerabilities in the software in your asset register.
Measure derivation
Derives measures from risks, audits and incidents.
Policy assistant
Writes policies that fit your standards and your company.
All assistants and roadmap
Principles, data protection and what comes next.
Start for free. Grow with us.
Essentials
All core modules incl. AI assistants
Advanced
All modules, incl. audits, BCM and playbooks
Enterprise
More than 25 users or several installations within a group
The free edition is free of charge for good. Cloud hosting in Germany, SSO & REST API and onboarding are available as options.
Built by practitioners, not by a marketing department.
Ready for an ISMS without the ballast?
Start with the free edition or let us show you WolfISMS in a demo.